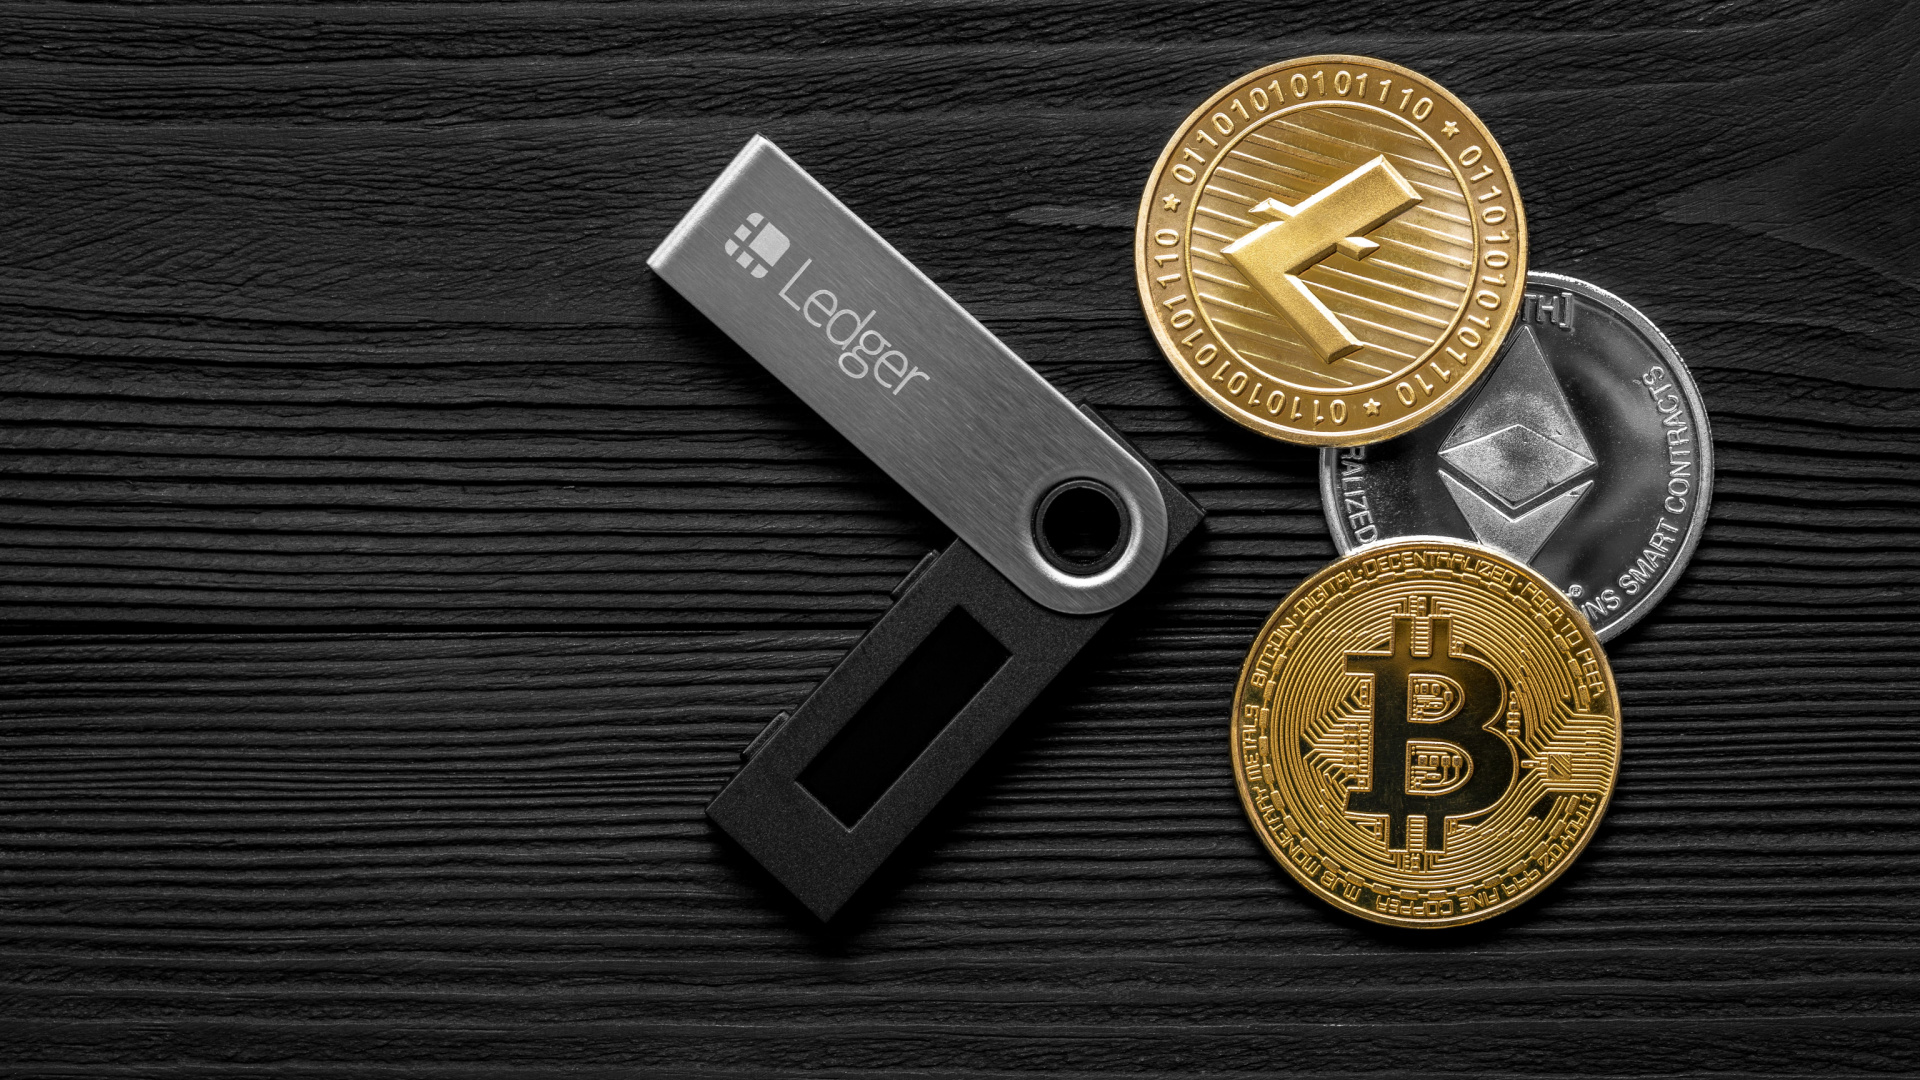
Ledger revealed a months-long operation by an organized crime group that installed malicious hardware in genuine wallets, and asked authorized sales channels in Southeast Asia and Hong Kong to temporarily suspend sales.
According to updated investigation findings reported by Wu Blockchain, the attackers bought and dismantled genuine Ledger devices and installed custom hardware designed to capture recovery phrases. The tampered wallets were then distributed through resale channels in Southeast Asia.
Ledger said the group had built multimillion-dollar infrastructure to capture recovery phrases, drain users’ assets, and launder illicit proceeds. Stealing these phrases, which enable access to the wallet, directly puts users’ crypto assets at risk.
Retailers instructed to suspend sales and not resell returned devices
The company asked authorized retailers and distributors in Southeast Asia and Hong Kong to temporarily suspend all sales. Under new security rules, devices may not be kept on open shelves or in display areas.
Retailers were instructed not to put returned devices up for resale. The measures therefore cover not only suspending sales but also storing products and handling returns.
Ledger says attack occurred through third-party distribution channels
Ledger reported that the incident was an attack targeting local third-party distribution channels. According to the company, the secure element chips, BOLOS operating system, and its own server infrastructure were not affected.
The updated findings describe a method in which genuine devices were altered during distribution and put back on the market. Suspending sales and not reselling returned products are also among the measures addressing this distribution risk.
Not investment advice.